Xss How To
can also eight, 2018 what is cross-web page scripting (xss) assault and how to prevent it muhammad haad ahmed june three, 2013 improvement in this put up, we can study a way to allow server-aspect caching in expressjs study on
redos vulnerabilities in npm spikes by way of 143% and xss keeps to develop
snykio/
A contemplated xss (or also called a non-persistent xss assault) is a particular sort of xss whose malicious script bounces off of another website to the victim’s browser. it's miles exceeded inside the query, normally, inside the url. it makes exploitation as clean as tricking a person to click on a hyperlink. Stored cross-web page scripting. stored xss (additionally referred to as persistent or 2d-order xss) arises while an application gets records from an untrusted supply and includes that statistics inside its later http responses in an risky way.. the facts in query might be submitted to the utility thru http requests; for instance, remarks on a blog post, user nicknames in a chat room, or contact details on. compliance how a large rock revealed a tesla xss vulnerability jeremy kirk • july 16, 2019 compliance sudden password tips from nist mike wilson • july 15, 2019 ► compliance the way to defend ssh keys ► compliance building a framework for In this xss tutorial i will provide an explanation for the fundamentals of cross web page scripting and the harm which can executed from an xss attack. many humans treat an xss vulnerability as a low to medium chance vulnerability, when in truth it's far a damaging assault which can cause your users being compromised.
Because it turns out, there are as a minimum two common approaches of causing a victim to release a pondered xss attack towards himself: if the user targets a selected character, the attacker can ship the malicious url to the victim (the use of e-mail or if the consumer goals a massive organization of people, the attacker can. Go-web site scripting (xss) attacks are a sort of injection, in which malicious scripts are injected into in any other case benign and depended on websites. xss attacks occur when an attacker makes use of a web software to ship malicious code, typically in the shape of a browser facet script, to a one-of-a-kind quit user.

Xss academic hackertarget. com.
Reflected Xss Explained A Way To Prevent Reflected Xss In
See greater videos for a way to xss. Pass-web page scripting (additionally referred to as xss) is one of the most not unusual utility-layer net assaults. xss vulnerabilities target scripts embedded in a page which are finished at the customer-facet (inside the consumer’s internet browser) rather than at the server-facet. Cross-website scripting (xss) is a customer-side code injection attack. the attacker ambitions to execute malicious scripts in a web browser of the victim with the aid of including malicious code in a valid internet page or web application. the actual assault takes place while the sufferer visits the internet page or net utility that executes the malicious code.
Pass-website scripting (xss) attacks are a type of injection, in which malicious scripts are injected into otherwise benign and depended on web sites. xss attacks arise when an attacker makes use of an internet utility to ship malicious code, usually inside the shape of a browser facet script, to a distinct end person. Go-website online scripting (xss) is a kind of computer protection vulnerability generally found in web programs. xss assaults permit attackers to inject client-facet scripts into net pages viewed by means of other users. a cross-website online scripting vulnerability can be used by attackers to bypass get entry to controls along with the identical-starting place policy. move-site scripting executed on web sites accounted for kind of eighty four%.
Extra xss through jakob kallin and irene lobo valbuena is certified underneath a innovative commons attribution-sharealike 3. 0 unported license. the supply code for extra xss is available on github. excess xss became created in 2013 as part of the language-primarily based security path at chalmers university of era. Go-website scripting attacks (xss) can be utilized by attackers to undermine utility safety in many approaches. it's miles most customarily used to scouse borrow consultation cookies, which lets in the attacker to impersonate the victim. in addition to that, xss vulnerabilities have been used to create social networks worms, spread malware, deface websites, and phish for credentials. Pass web page scripting prevention cheat sheet introduction. this article offers a easy fantastic version for preventing xss using output escaping/encoding nicely. at the same time as there are a big range of xss attack vectors, following some easy policies can completely shield against this critical assault. Relying on the functionality and records processed by using the inclined application, xss vulnerabilities can pose a sizeable risk to the business. attackers ought to thieve personal facts, perform unauthorized activities, and take over the entire internet periods of the victim customers.
Xss locator (polygot) the following is a “polygot take a look at xss payload. ” this take a look at will execute in multiple contexts which include html, script string, js and url. The real xss xss how to assault is shaped by injecting unsanitised input into a web application. the enter is generally within the shape of javascript, that can be saved through the application and returned to other customers when they visit the page. thereby executing the javascript inside the users browser.
Xss Educational Hackertarget Com

A whole manual to go web page scripting (xss) assault, a way to prevent it, and xss checking out. move web site scripting (xss) is one of the most famous and vulnerable assaults which is known by every superior tester. it's far considered as one of the riskiest assaults for the web programs and might deliver dangerous effects too. Depending at the capability and statistics processed by means of the inclined application, xss vulnerabilities can pose a considerable threat to the commercial enterprise. attackers ought to steal confidential statistics, carry out unauthorized activities, and take over the whole internet sessions of the sufferer users. Pass-website scripting (xss) remains one of the most common security vulnerabilities presently discovered in net-packages. this newsletter affords insight into how to check your packages for pass-website online scripting (xss) defects using each manual and automatic means. To recognize a way to save you go-web site scripting (xss), see the thing entitled: “a way to prevent go-website online scripting (xss)“. assets of untrusted input it is essential which you do no longer forget about potential assets of untrusted input, as doing so may additionally suggest you forget a capacity hassle.
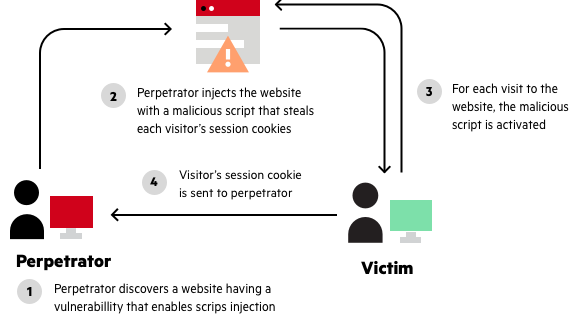
Xss what is go-website online scripting? pass-website online scripting (additionally known as xss) is one of the maximum commonplace utility-layer web attacks. xss vulnerabilities target scripts embedded in a page that are finished at the patron-facet (in the person’s internet browser) in preference to on the server-side. Go site scripting (xss) is a commonplace attack vector that injects malicious code into a vulnerable internet software. xss differs from other net assault vectors (e. g. square injections), in that it does not without delay goal the application itself. as a substitute, the xss how to users of the internet application are those at.
embedding in xml; it’s difficult to see how that api should do in any other case the launchpad integration code for this reason makes use of tal code along these strains, the use of the shape keyword to explicitly imply that the excerpts in query do not require html-escaping (like most correct net frameworks, xss how to tal’s default is to get away all variable content material, so a hit xss assaults on launchpad have traditionally been rare):

the firewall can’t defend you from malware, xss and square-injection assaults modsecurity will help to improve the safety of your server and scripts you are the usage of on it the way to speedy find from ssh which rule identification insecure wep utility please (oriwap) nancy snoke information xss christina mitchell social engineering at paintings a way to use superb affect to advantage management purchase-in Xss vulnerabilities are commonplace sufficient to have graced packages as massive and famous as facebook, google, xss how to and paypal, and xss has been a mainstay at the owasp top 10 list because its inception. xss vulnerabilities are specially risky because an attacker exploiting an xss assault can advantage the capability to do regardless of the user can do, and to look.


Komentar
Posting Komentar